TL;DR
All data destruction companies will tell you they are certified. The useful comparison is narrower: can they give you per-serial evidence, can they account for the device from collection onwards, and can they name the sanitisation method they apply.
- A certificate without serial numbers cannot be matched to your register.
- Ask which method and against what guidance, not whether they comply.
- Transport is the least evidenced link in the chain.
- Verified wiping usually beats shredding, for cost and for reuse.
- The cupboard of old laptops is the real risk, not next month’s leaver.
- Record disposal as a status with evidence, never as a deleted row.
When you do not need a vendor yet
Four stages, and the first does not need procurement.
A handful of devices, all in one place. Built-in encryption plus a verified erase from the operating system is a reasonable position, documented. You do not need a contract for three laptops.
Best tools for Device Management
Devices accumulating but nothing leaving. The exposure is growing and nobody has processed anything. This is the point to write the process, before volume forces an improvised answer.
Regular departures, distributed team. Devices are now in places you cannot reach, and the transport question becomes the whole question. A vendor relationship starts earning its cost here.
Audited, certified or contractually obliged. Somebody external will ask for evidence per device. Now the certificate format matters as much as the method.
What data destruction companies are actually selling
Three different things, sold under one heading, and the confusion is why comparisons go wrong.
The first is the physical act: wiping or destroying a drive. This is the least differentiated part. The methods are published, the equipment is widely available, and almost any serious vendor can do it correctly.
The second is custody. Where was the device between leaving somebody’s desk and arriving at the facility, and who could have opened the box. This is where real differences live, and it is the part most proposals describe in the vaguest language.
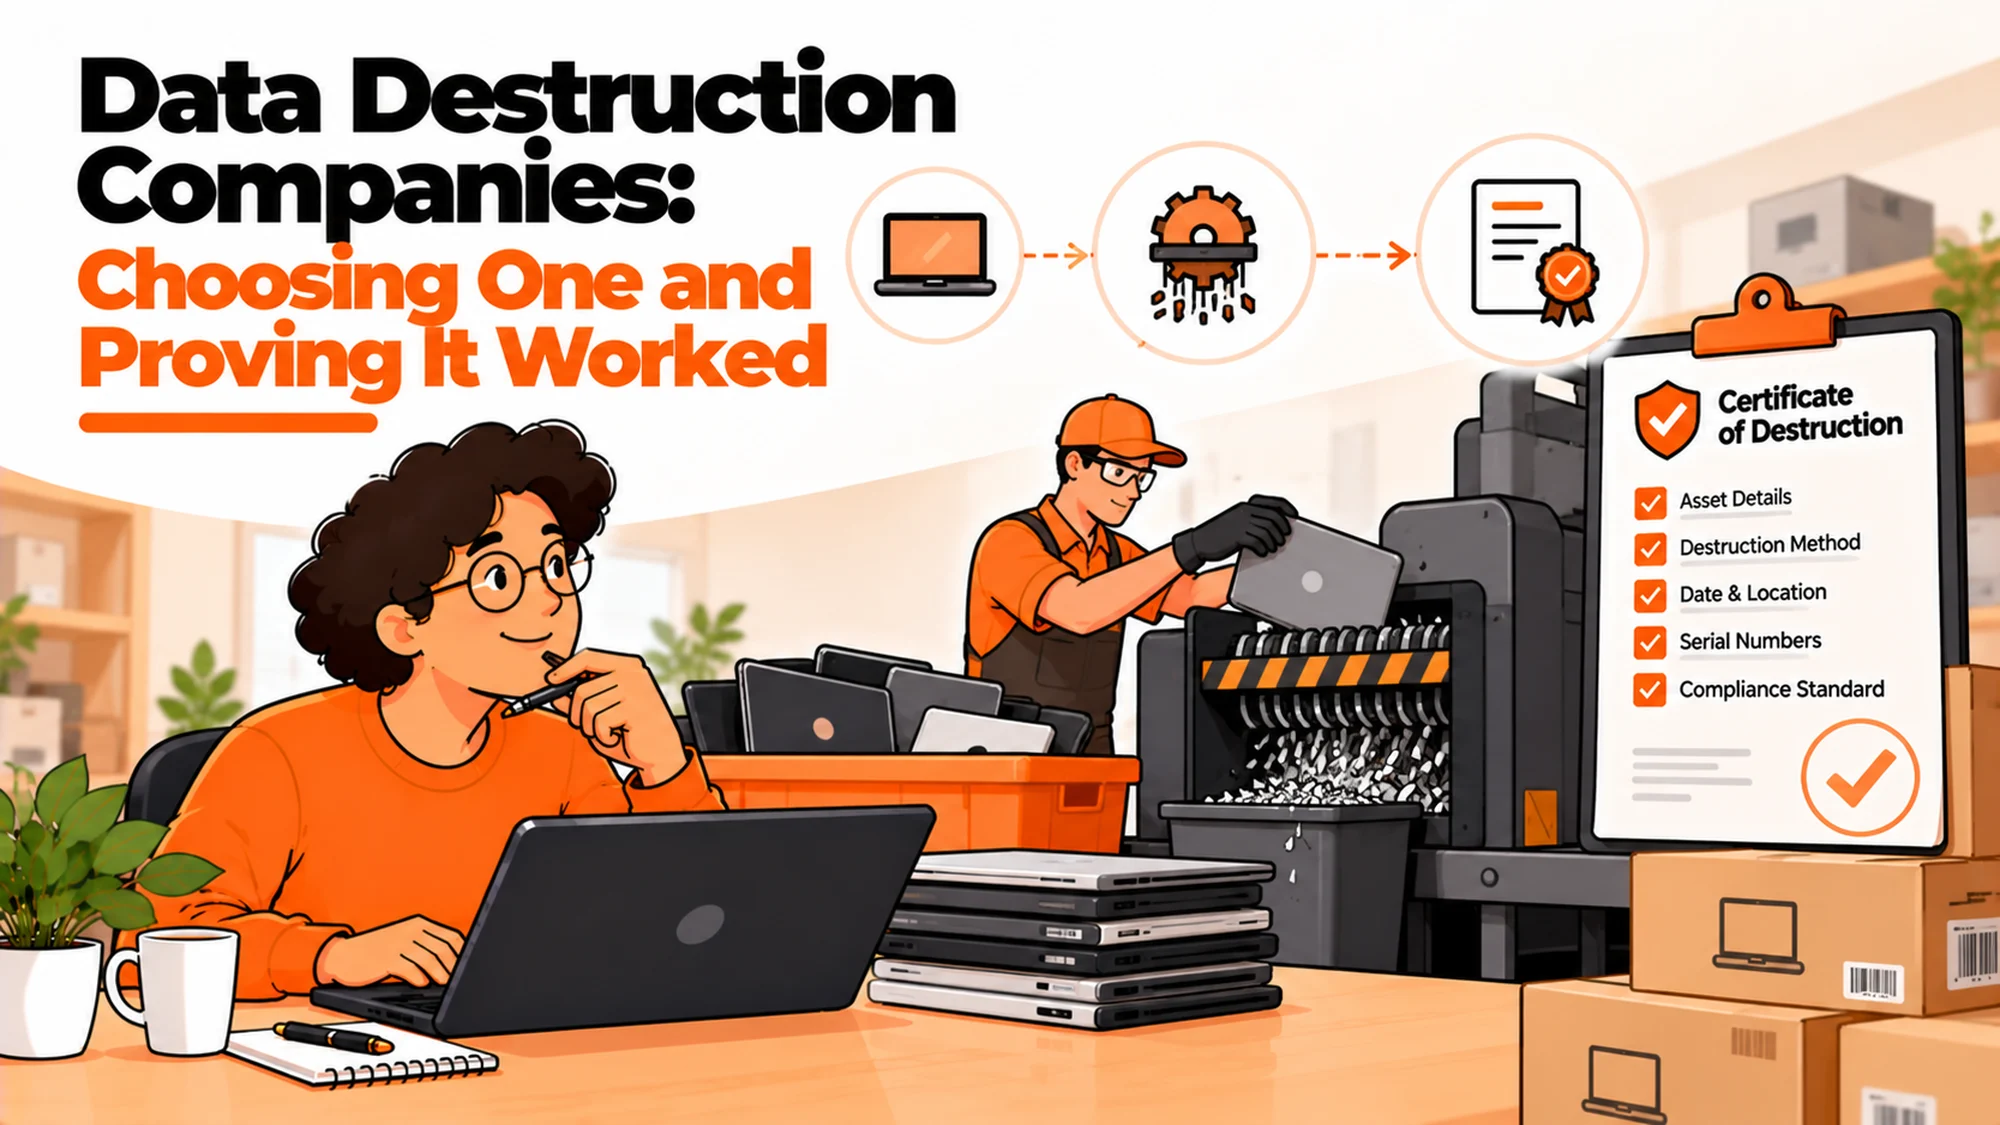
The third is evidence. A document you can hand to an auditor that ties a specific serial number to a specific method on a specific date. Plenty of vendors produce a certificate. Fewer produce one that reconciles against an asset register without manual work.
Media sanitisation guidance such as NIST SP 800-88 sets out the methods and, importantly, the verification step that distinguishes a completed sanitisation from an attempted one. And the equipment itself is regulated waste at end of life: the EU framework for waste electrical and electronic equipment governs what happens to the hardware after the data is gone, which is a separate obligation from the data one and often handled by a different part of the same vendor.
The six questions that separate them
- Will the certificate list serial numbers? If the answer is a quantity, you cannot reconcile it. This question alone filters most of the market.
- Who holds the device in transit, and what is logged? Ask for the tracking record from a real past job, not the process description.
- Which sanitisation method, and verified how? A named method plus a verification step. Vagueness here is the answer.
- What happens to a drive that fails verification? There should be a defined fallback to physical destruction, recorded differently.
- Can you collect from a home address in the countries we employ in? Most capability claims thin out at this question.
- What is the evidence format? A PDF per device is common and painful at volume. Ask what reconciles against a register.
Six questions, and you can ask all of them in one call. The pattern worth watching is which ones get a specific answer and which get reassurance.
Five questions about your own situation
How many devices are already sitting unprocessed? That backlog, not your future flow, usually sets the scope of the first job.
Where are your people? A vendor strong in one market may need to subcontract elsewhere, which changes the custody chain.
Do you want devices back or gone? Reuse, resale and destruction are different services and mixing them in one brief produces a confusing quote.
Who will hold the evidence? A named owner and a place it lives, or certificates accumulate in an inbox.
Can you list what you hold right now? If not, fix that first, because you cannot evidence the destruction of a device you never recorded.
Types of provider, and the trade-offs
On-site shredding. Best when transport risk is unacceptable and devices are in one building. It struggles on cost per device, on distributed teams, and it destroys residual value that could have been recovered.
Off-site facility with collection. Best for volume and for cost. It struggles exactly where the collection is weakest, since the transport leg is both the riskiest and the hardest to evidence.
Recycling and waste specialists. Best on the environmental obligation and on bulk hardware. They struggle on data evidence, because the discipline is waste handling and per-serial data certificates are not the native output.
Do it yourself with built-in tools. Best for small numbers and for control. It struggles on evidence and on failed drives, and it quietly depends on somebody remembering to do it.
A lifecycle service that collects and wipes. Disclosure: RemoAsset is owned by the same people who publish this site. It handles retrieval, storage and certified wiping across 80 or more countries, which matters here because the collection leg and the destruction are then one tracked job rather than two vendors meeting in the middle. Where it struggles: it is not a bulk waste contractor, so a datacentre decommission or a pallet of old servers is the wrong fit. The narrow thing it changes is whether the device reaches the wipe at all, which is the failure mode that actually occurs.
The decision table
| Situation | Scale | Setup | Primary pain | Recommended starting point |
|---|---|---|---|---|
| Few devices, one site | Under 10 | No IT owner | No process | Verified erase, documented |
| Backlog in a cupboard | Any | Any | Live data, no custody | Clear the backlog as one job |
| Regular remote leavers | 50 plus | One IT owner | Devices never collected | Fix collection before method |
| Audit asks per device | Any | Security owner | Certificates lack serials | Change vendor or evidence format |
| Several countries | 100 plus | IT team | Coverage claims thin out | Test one collection per market |
| Bulk hardware retirement | Any | Any | Volume and waste rules | A waste specialist, separately |
What getting this wrong costs
The first cost is the evidence you cannot produce. Asked to show that a specific laptop was sanitised, a team with quantity-based certificates has to argue by inference. That argument is weak precisely when it matters, which is after an incident rather than before one.
The second is paying for the wrong service. Shredding a three-year-old laptop that would have passed verification and resold is money spent to destroy value, twice over. The method should follow the risk assessment, and when it does not, the default is usually the expensive one.
The third is the backlog nobody owns. Devices in a cupboard are the clearest unmanaged exposure in most organisations: live data, no custody record, no owner, and no event scheduled that would cause anybody to deal with them. It persists because it is nobody’s current problem.
The fourth is the gap this article keeps returning to. Destruction is the easy half. Collection is the half that fails, and a device that never arrives cannot be wiped by the best vendor in the market.
So the question worth asking is not which vendor destroys data most thoroughly. It is how many of your retired devices actually reach one.
When the gap is collection, not destruction
Most teams shopping for a destruction vendor have a collection problem wearing a destruction problem’s clothes.
Three signals tell you which one you have. The number of devices you processed last year is lower than the number of people who left. Returns from outside your main market took weeks or never completed. And your unprocessed pile is growing faster than your disposal record.
If any of those is true, a better destruction vendor changes nothing, because the devices are not reaching the current one either. The constraint is upstream and it is logistical.
Worth establishing before you run a procurement exercise, since the answer changes what you are buying. Looking at how collection, storage and certified wiping fit into one record settles whether you need a destruction vendor, a retrieval route, or both.
See how wipe certificates attach to asset records
Read our guide to equipment compliance evidence
Related reading
- Evidencing equipment compliance
- The data protection policy
- IT asset recovery
- Unreturned equipment
- Equipment and ESG reporting
Frequently Asked Questions
What should a certificate of destruction contain?
The serial number of each device, the method used, the date, and who performed it. A certificate listing a quantity rather than serials cannot be matched to your asset register, which means it proves something happened without proving it happened to your laptop.
Is wiping as good as physical destruction?
For most modern drives a verified sanitisation is appropriate and lets the device be reused or resold, which is both cheaper and better environmentally. Physical destruction is the right answer when a drive has failed, cannot be verified, or your own risk assessment requires it. The method should follow the situation, not a default.
Do I need an on-site service?
On-site removes the transport risk, which is the part of the chain most often unevidenced, but it costs more and does not suit distributed teams. For remote staff an off-site service with tracked collection and per-serial certificates is usually the practical answer, provided the tracking is real rather than described.
What standards should I ask about?
Ask which sanitisation method they apply and against what published guidance, rather than asking whether they are compliant. NIST SP 800-88 is the common reference for media sanitisation. A vendor who can name the method and the verification step is a different proposition from one who answers with a logo.
Who is responsible if the vendor fails?
You remain accountable for your own data, which is why evidence matters more than assurance. Using a vendor transfers the work and not the responsibility. The practical consequence is that your records of what you sent and what came back are the thing you will be asked for.
What about devices still in storage?
They are the biggest unmanaged risk in most organisations. A cupboard of old laptops nobody has processed holds live data under no custody at all. Clearing that pile is usually the highest value first project, ahead of refining the process for new departures.
Does disposal need to be in the asset register?
Yes, as a status with the evidence attached rather than as a deleted row. A device removed from the register with no disposal record looks exactly like a device that went missing, and the two need to be distinguishable when somebody asks a year later.